Choosing a Website Platform: Why Managed SaaS Should Usually Be the Default
Squarespace, Webflow or WordPress? Why a managed platform should usually be the default, what plugins really cost you, and when WordPress is still worth it.
October 19, 2026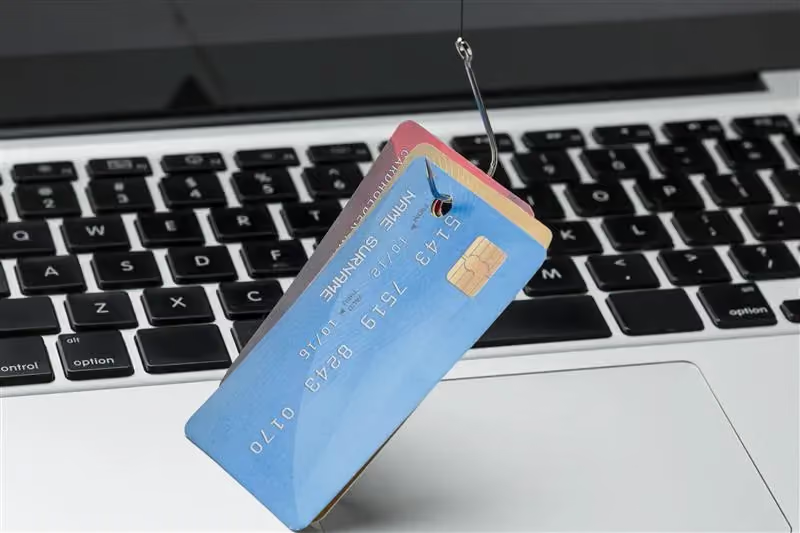
Cybersecurity is a shared responsibility, and one of the most common threats facing individuals and organizations today is phishing. These deceptive emails are designed to trick recipients into revealing sensitive information, such as login credentials, financial data, or personal details. With phishing attacks becoming more sophisticated and frequent, it's crucial to stay informed and vigilant.
In this guide, we’ll walk you through how to recognize phishing emails, what to do if you’ve accidentally shared your credentials, and how to report suspicious messages in Microsoft Outlook. Whether you're working remotely or in the office, these steps will help you protect yourself and your organization from cyber threats.
Phishing is a type of cyberattack where attackers impersonate legitimate entities to deceive recipients into clicking malicious links, downloading harmful attachments, or providing sensitive information. These emails often appear to come from trusted sources—like your bank, employer, or even a colleague—but they’re designed to exploit your trust.
Common Phishing Tactics Include:
If you suspect that you may have accidentally given out your email password or other sensitive information to a phishing scam, act immediately.
What to Do:
Quick action can prevent further damage and help secure your account before attackers gain full control.
Microsoft Outlook offers built-in tools to help users report suspicious emails. Reporting phishing attempts not only protects you but also helps Microsoft improve its filters and safeguard others.
Reporting phishing emails is more than just a personal safety measure—it’s a way to protect your entire organization.
Benefits of Reporting:
Phishing prevention starts with awareness. Here are some best practices to help you and your team stay secure:
To help you recognize phishing attempts, here are a few examples of what they might look like:
Subject: “Action Required: Your Microsoft Account Will Be Locked”
Body: “We noticed unusual activity. Please verify your account immediately.”
Link: Redirects to a fake login page that steals your credentials.
Subject: “Urgent Request from John P. Shoff”
Body: “Canyou send me the client list ASAP? I’m in a meeting.”
Sender: A spoofed email address pretending to be your manager.
Subject: “Invoice #84729 Attached”
Body: “Please see the attached invoice for your recent purchase.”
Attachment: Contains malware that infects your device.
If you’re ever uncertain about an email, don’t take risks. Instead:
Phishing attacks are constantly evolving, but with the right knowledge and tools, you can stay one step ahead. By recognizing the signs, reporting suspicious emails, and practicing good cybersecurity habits, you help protect not only yourself but your entire organization.
Remember: Cybersecurity is a team effort. Stay informed, stay cautious, and don’t hesitate to ask for help when something feels off.
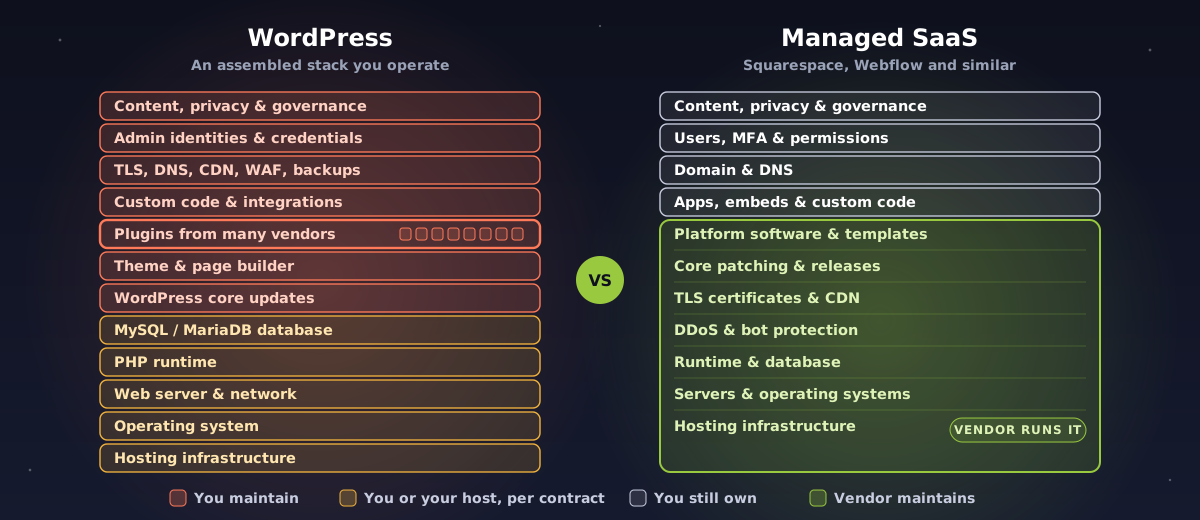
Squarespace, Webflow or WordPress? Why a managed platform should usually be the default, what plugins really cost you, and when WordPress is still worth it.
October 19, 2026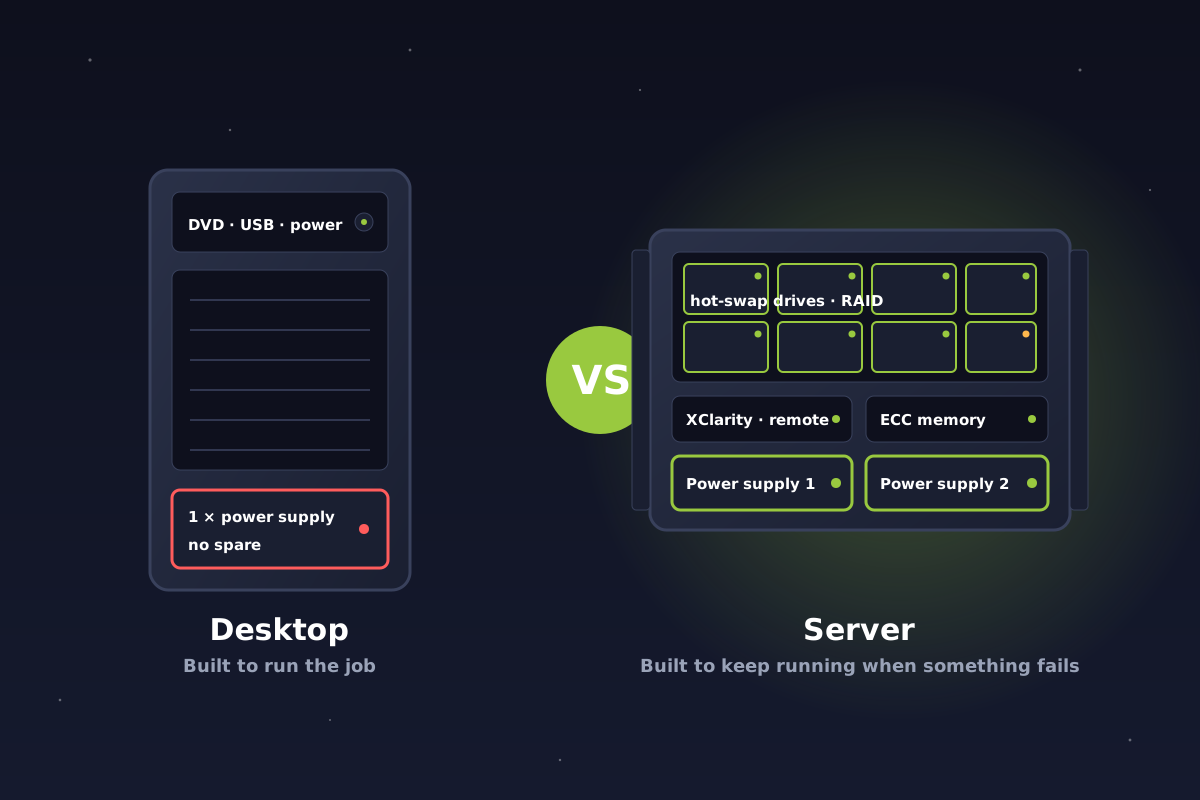
Can a desktop be your server? It can, but it shouldn't always be. See why Lenovo ThinkSystem servers win on reliability, redundancy, remote management and downtime.
October 14, 2026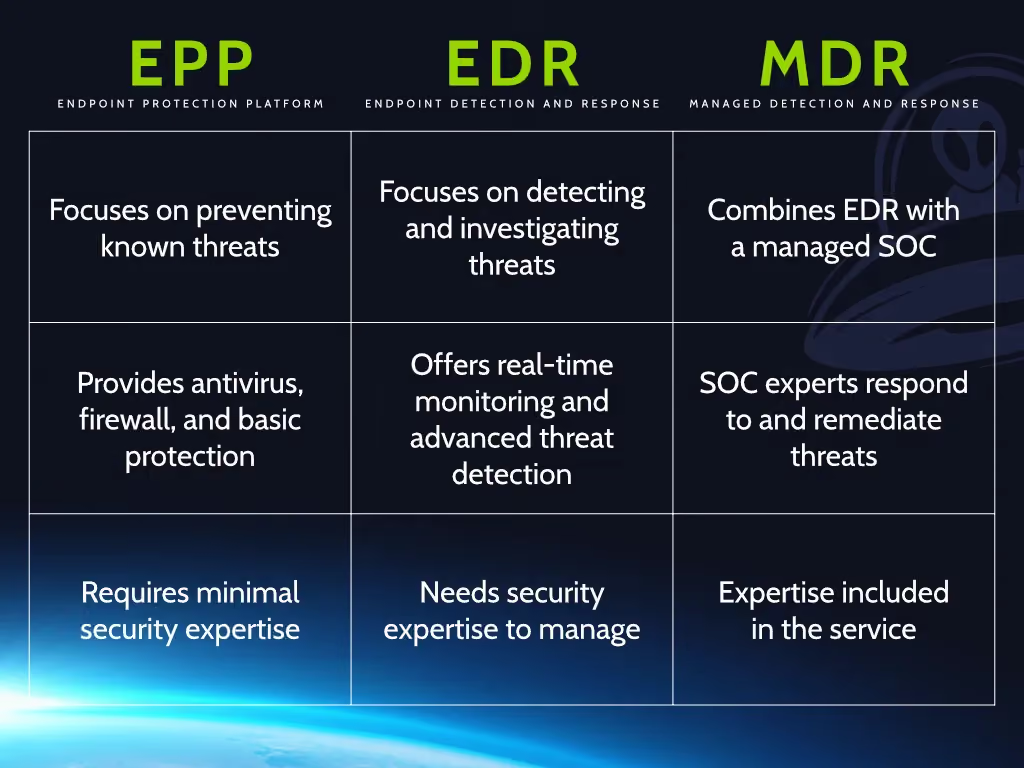
Antivirus, EDR and MDR explained in plain language, and why antivirus alone no longer protects Alberta and Canadian businesses from ransomware and modern attacks.
October 13, 2026